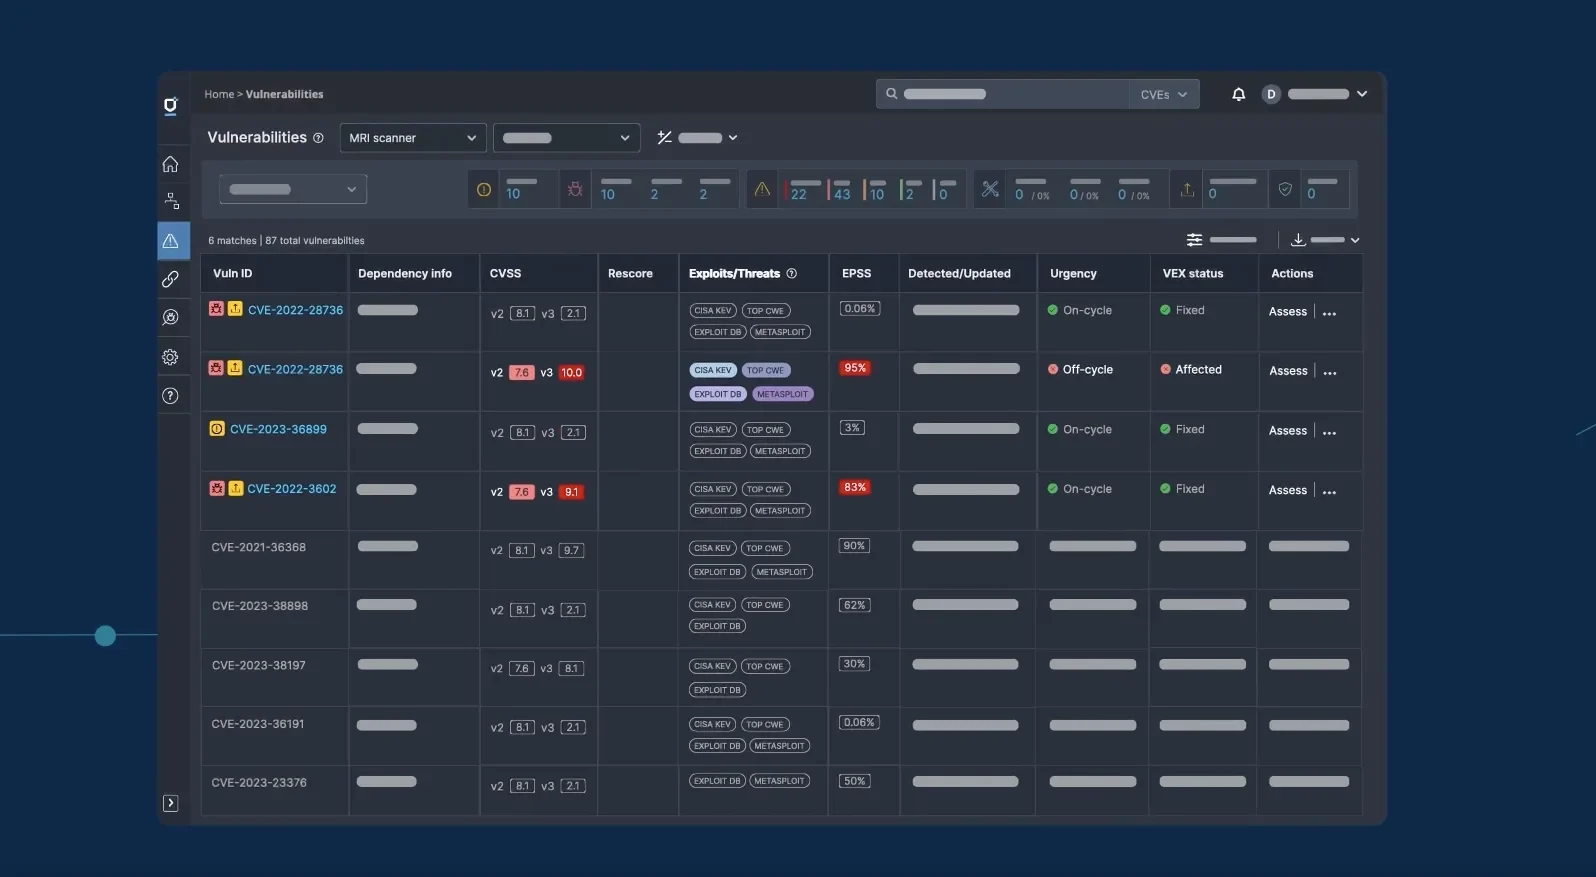
The FDA’s cybersecurity guidance for medical devices requires both processes and technology tools to ensure products are secure by design and resilient in the field. This whitepaper explores how manufacturers can build a mature cybersecurity program that meets regulatory expectations while minimizing long-term costs and risks. Using a hypothetical device manufacturer as an example, it breaks down FDA’s premarket and postmarket recommendations, maps them to practical workflows, and highlights leading software tools (including Medcrypt) that help address the technical requirements for vulnerability management, encryption, and risk monitoring.